We are a digital agency helping businesses develop immersive, engaging, and user-focused web, app, and software solutions.
2310 Mira Vista Ave
Montrose, CA 91020
2500+ reviews based on client feedback
What's Included?
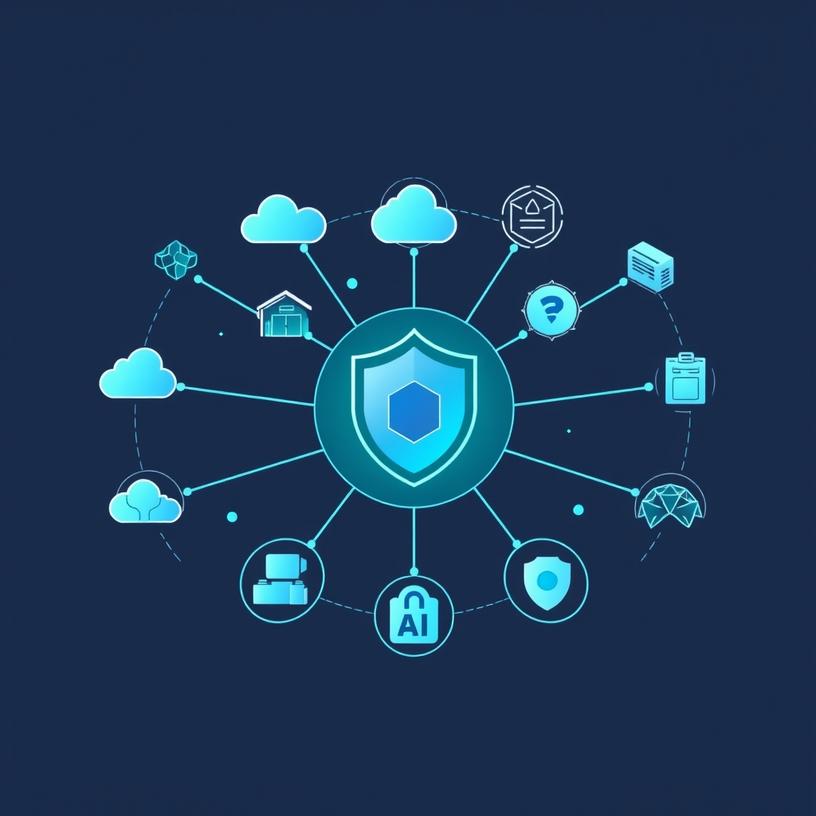
ToggleBig tech players are lining up guardrails for AI work that runs in the cloud. CrowdStrike Holdings, a name security teams trust, is joining Blueprint Alliance as a founding member. The move signals that securing AI agents, the small programs that run tasks across devices and clouds, is becoming a top priority for major vendors. The blueprint aims to set shared standards and practical tools so vendors can work together to defend agents from tampering, data leakage, and impersonation. For CrowdStrike, this is more than a vanity signup. It places the company at the center of how enterprises will manage security as AI agents spread across multi cloud setups.
People think of agents as chatty bots, but the reality is broader. AI agents include code that runs on endpoints or in the cloud and acts on data with little human input. They can collect data, make decisions, or automate workflows. When you have dozens or hundreds of agents across AWS, Google Cloud, and private networks, the attack surface grows. A compromised agent could steal data, move laterally, or seed bad instructions. The Blueprint Alliance wants to harden the agent lifecycle with secure code, trusted runtimes, encrypted channels, and continuous monitoring. CrowdStrike adds strong telemetry, threat detection, and incident response to this mix, so agents stay safer in real-world use.
For organizations, this alliance could reduce gaps when AI work runs across multiple clouds. If the alliance delivers shared baselines, customers get consistent policy enforcement, easier audits, and better visibility into what each agent can do. It could also speed up threat-hunting across ecosystems because defense signals become more interoperable. In practice, that means fewer surprises during incident response and smoother compliance. But it also means buyers should watch for potential lock-in if tools tilt toward Blueprint certified paths. So far the emphasis is on interoperability and trust, not on locking customers into a single vendor. In the end, enterprises win when security keeps pace with automation instead of slowing it down.
From a market view, the move nudges security toward easier cross cloud protection. For CrowdStrike, the alliance broadens its reach beyond devices to cloud and identity contexts. It can help win larger deals where CIOs want a single view of risk across platforms. Competitors will watch closely because once a standard sticks, customers gravitate toward ecosystems that fit it. The Blueprint Alliance could also shape security budgets and service levels, since vendors share responsibilities. On the downside, vendors worry about compatibility gaps and the cost of cross-vendor support. Still, doing this as a group lowers the cost of point solutions and may speed up the adoption of safer AI practices.
Security collaborations work best when there are clear rules for data sharing, ethics, and governance. Key questions: Who sets the security baseline and how often is it updated? How is threat intelligence exchanged and who owns it? Will customers control what data is shared across vendors? And how does privacy fit when AI agents handle sensitive data? The alliance should avoid stifling competition or building a fixed list of approved tools. Instead, it should offer transparent standards, open testing, and options for vendors to extend capabilities without breaking compatibility. The bigger risk is complacency. If participants lean on the alliance as a shield, they may miss evolving threats from smarter AI, misconfigurations, or supply-chain flaws.
I see this as a careful bet on safer AI-enabled workflows. The real value will show up when the Blueprint Alliance defines practical, usable standards and tests them in real deployments. For CrowdStrike, expect closer ties with cloud and identity partners, more integrated threat detection, and a clear picture of return on security investments. For buyers, the focus should be on vendors that commit to shared standards and measurable security outcomes, not flashy claims. In the long run, a strong alliance can push the market toward safer AI adoption, helping teams use AI with less risk. The road ahead is not simple, but moving forward together makes sense.
Comments are closed